Category: Malware Analysis
-
NanoCore Screen Exfiltration — The Rat That Filmed Its Own Jail
A 58 KB NanoCore RAT takes a 1920×1080 screenshot every 30.7 seconds, base64-encodes it, and POSTs it back to its command and control server in plaintext HTTP — five times in two and a half minutes, all of it inside a 1.5…
-
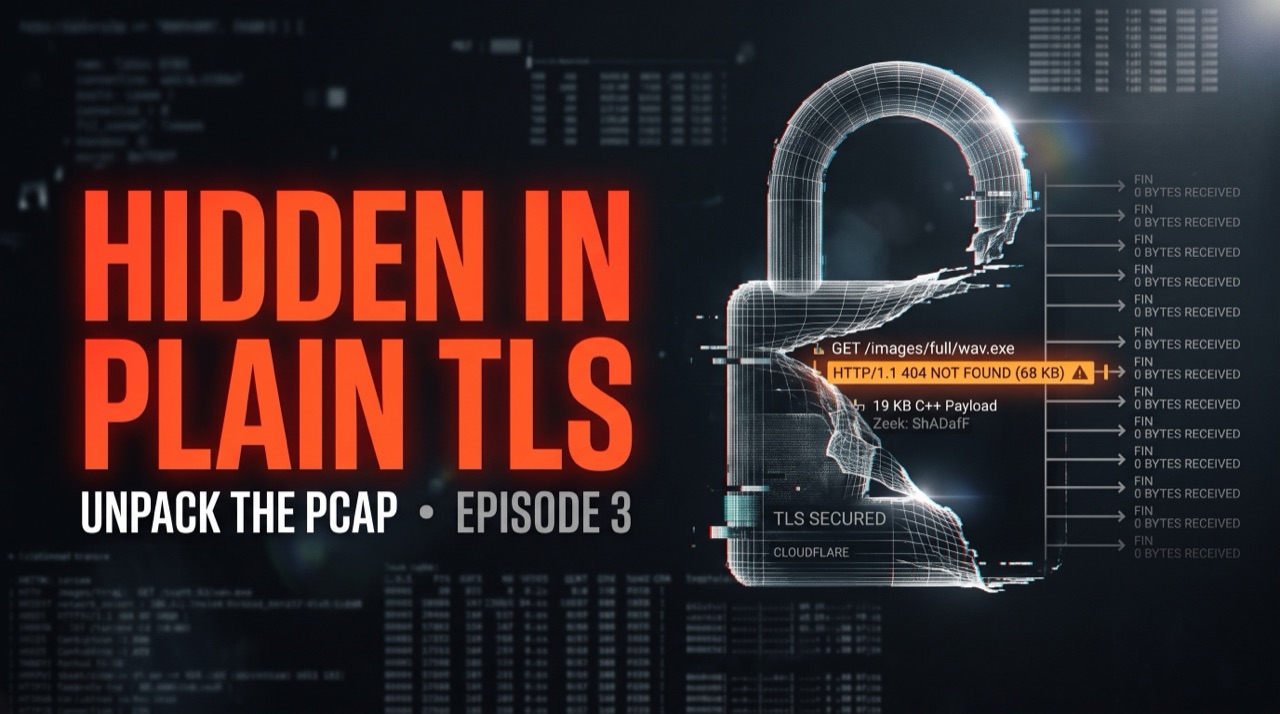
Waski Downloader — Cloudflare Payload, Silent Callbacks
A 19 KB C++ trojan downloader drops a child process, wraps its payload fetch in a valid Cloudflare-fronted TLS session, and produces exactly zero certificate errors in 150 seconds of traffic. Then it requests /images/full/wav.exe — an executable named like an audio…
-
Polish “Powiadomienie” JS Campaign — Credential Theft via FTP Exfiltration
A 3.6 MB JavaScript file, hardened with `javascript-obfuscator` — rotated string arrays, index decoders, 53 dead dispatcher functions, a catastrophic backtracking regex trap — ends with a plaintext FTP upload of your saved browser passwords. The entire malicious activity: 3 seconds. Join…
-
The 1.7 MB CAPTCHA — How a Fake Human Verification Check Delivered Two RATs
A fake CAPTCHA — 1.7 MB of React 19 served from a .top domain — tricks a visitor into pressing Win+Rand pasting PowerShell. No browser sandbox escape needed. No exploit. Just social engineering. What follows is a 6-stage infection chain: The full…
-
Hunting Lazy OPSEC: Spotting Default C2 Certificates with DuckDB and Zeek
Threat actors love to reuse tools, and sometimes, they get lazy. Case in point: AsyncRAT and its notorious fork, DcRAT. These remote access trojans often ship with default, self-signed certificates. If the operators don’t bother to swap them out before deploying their…
-
Detect STRRAT Malware With Zeek And Suricata
Join me in learning how to detect the STRRAT malware family with Zeek and Suricata. Corelight Blog: https://corelight.com/blog/newsroom/news/strrat-malware Source Code: https://github.com/corelight/zeek-strrat-detector 00:00:10:18 – 00:00:37:17Dr. Keith JonesHey, welcome. We’re going to talk about how to detect STRRAT, which is a malware family. This…
-
Detect Gozi Banking Malware With Zeek!
Join the Old Grizzled FBI Agent to hear how to detect the Gozi Banking Malware Family with Zeek! Corelight Blog: https://corelight.com/blog/gozi-banking-malware Transcript: 00:00:10:47 – 00:00:41:11Old Grizzled FBI AgentHi there. This is your favorite obligatory grizzled FBI agent again. You may wonder why…
-
Detecting AsyncRAT Malware C2 With Zeek And Suricata
Please join the “Old Grizzled FBI Agent” to hear how you can detect the AsyncRAT malware family with Suricata and Zeek! Corelight blog: https://corelight.com/blog/newsroom/news/hunt-of-the-month-detecting-async-rat-malware Zeek: https://zeek.org/ Source code: https://github.com/corelight/zeek-asyncrat-detector Transcript: 00:00:00:10 – 00:00:31:31Grizzled FBI AgentHello. I’m your obligatory grizzled FBI agent. Never…
-
Analyzing QBot/QakBot Malware With Zeek
In this short article I’ll outline some analysis I performed on the QBot/QakBot malware family with Zeek. I took a look at the following PCAPs from this family of malware, hoping to make it into a Zeek Roulette: You will see that…
-
Detecting njRAT/Bladabindi Malware With Zeek – Zeek Roulette #1
Welcome to the first edition of Zeek Roulette, where I pick a random Zeek topic and try to solve it! For this article I picked njRAT malware from Any.Run and tried to write a detector for it. There is a copy of…


