Category: Unpack The PCAP
-
NanoCore Screen Exfiltration — The Rat That Filmed Its Own Jail
A 58 KB NanoCore RAT takes a 1920×1080 screenshot every 30.7 seconds, base64-encodes it, and POSTs it back to its command and control server in plaintext HTTP — five times in two and a half minutes, all of it inside a 1.5…
-
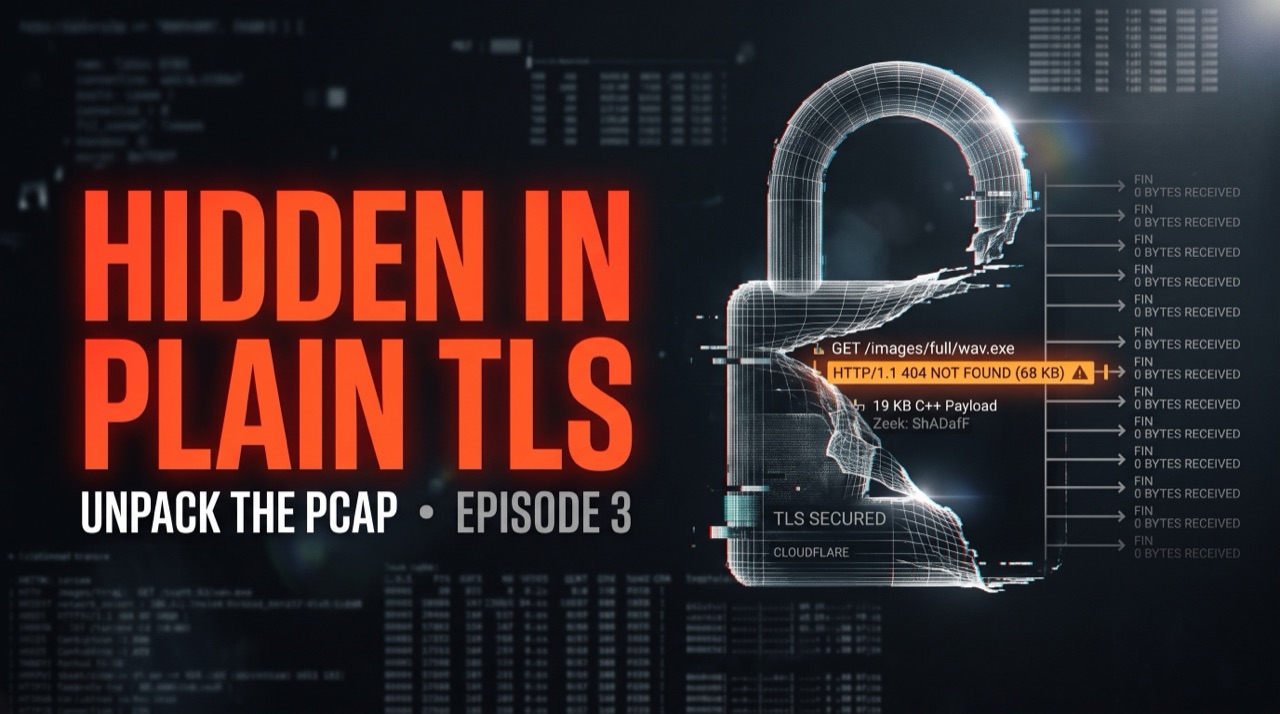
Waski Downloader — Cloudflare Payload, Silent Callbacks
A 19 KB C++ trojan downloader drops a child process, wraps its payload fetch in a valid Cloudflare-fronted TLS session, and produces exactly zero certificate errors in 150 seconds of traffic. Then it requests /images/full/wav.exe — an executable named like an audio…
-
Polish “Powiadomienie” JS Campaign — Credential Theft via FTP Exfiltration
A 3.6 MB JavaScript file, hardened with `javascript-obfuscator` — rotated string arrays, index decoders, 53 dead dispatcher functions, a catastrophic backtracking regex trap — ends with a plaintext FTP upload of your saved browser passwords. The entire malicious activity: 3 seconds. Join…
-
The 1.7 MB CAPTCHA — How a Fake Human Verification Check Delivered Two RATs
A fake CAPTCHA — 1.7 MB of React 19 served from a .top domain — tricks a visitor into pressing Win+Rand pasting PowerShell. No browser sandbox escape needed. No exploit. Just social engineering. What follows is a 6-stage infection chain: The full…


